Guide overview
EOR security evidence, at a glance.
Check scope, dates and issuer behind every assurance claim.
Check an EOR’s security evidence against the service, entities and employee data you will use. SOC 2 provides an assurance report; ISO 27001 concerns information-security management; GDPR certification, where claimed, needs an approved scheme and a defined processing scope. None of these establishes employment licensing or payroll accuracy.
SOC 2
Read the report
Check the stated period, scope and auditor’s evidence.
ISO certificates
Check current validity
Review the certified entity, scope, dates and issuer.
GDPR assurance
Check the scheme
Identify the approved certification scheme behind a claim.
Employment delivery
Review separately
Security assurance says nothing about payroll or employment compliance.
Check before acting
Request current documents and resolve evidence gaps before treating a badge as assurance for your hire.
What to record in the worksheet
Scope
Assurance claim · Document / link · Entity and service scope
Evidence and follow-up
Period / expiry · Exceptions / exclusions · Reviewer · Review outcome · Recheck date
What to do when the assurance evidence has a gap
When a document leaves part of your payroll service uncovered, write down what’s missing, what you’ve requested and who has authority to accept or reject the risk.
Start with the documents to request. Review each evidence type, then keep the outcome in the assurance-review register. A SOC 2 report, an ISO certificate and GDPR evidence answer different questions.
| What you receive | Check next | Decision to record |
|---|---|---|
What you receive
SOC 2 marketing statement
|
Check next
Obtain the report under agreed access terms; inspect system scope and dates.
|
Decision to record
Claim unverified until reviewed; do not infer a failed audit.
|
What you receive
Report excludes a service or partner
|
Check next
Identify the excluded work and request separate assurance.
|
Decision to record
Accept compensating evidence or hold that country’s approval.
|
What you receive
Audit period ended months ago
|
Check next
Ask about material changes and newer reports; review any management bridge letter.
|
Decision to record
Whether the evidence is recent enough for your risk policy.
|
What you receive
ISO certificate for a different entity
|
Check next
Match entity, sites, service scope, edition, issuer and validity.
|
Decision to record
Whether the employing/payroll operation is actually covered.
|
What you receive
Control exception or customer responsibility
|
Check next
Request remediation evidence and assign your own required controls.
|
Decision to record
Named owner, completion date and any accepted residual risk.
|
What you receive
GDPR or privacy badge
|
Check next
Identify the scheme, processing scope and legal roles.
|
Decision to record
Separate certification evidence from data terms and transfer compliance.
|
Review those separately for each country.
Identify the report type, period and named legal entities.
Check the actual employer and services used for your hire.
Confirm which activities and subcontractors are covered.
A badge or trust-platform logo does not prove coverage.
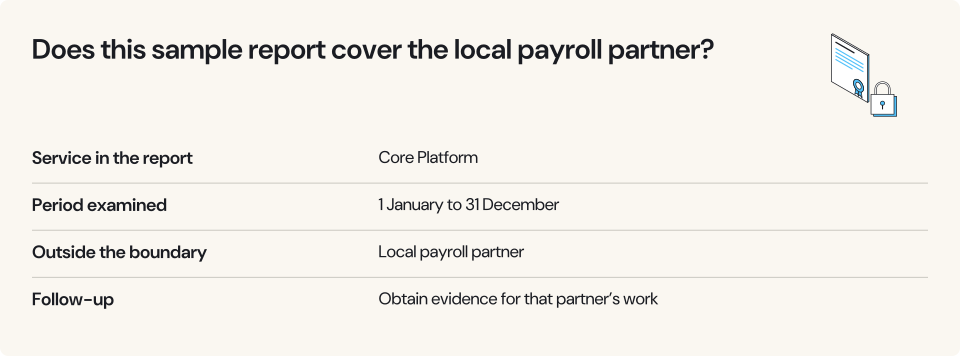
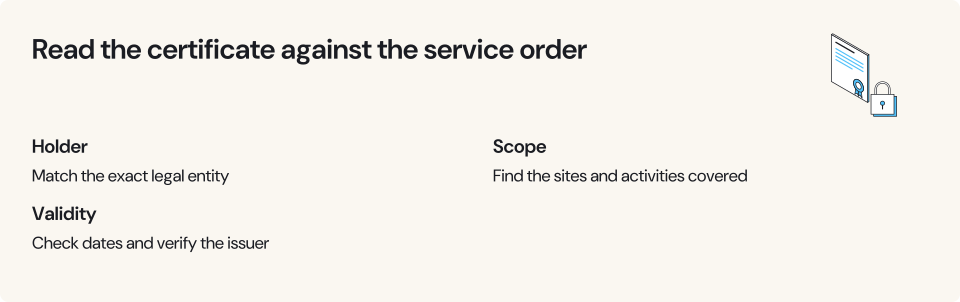
Illustrative scope check. A certificate or report covers its stated boundary; it does not automatically extend to every group company or partner.
1. Why an EOR needs a security review
Start with one employee’s data. Who receives their identity documents and bank details? Where do tax records and benefits information go, and which local payroll or benefits partners have access? Map those transfers before deciding which documents to request from the EOR.
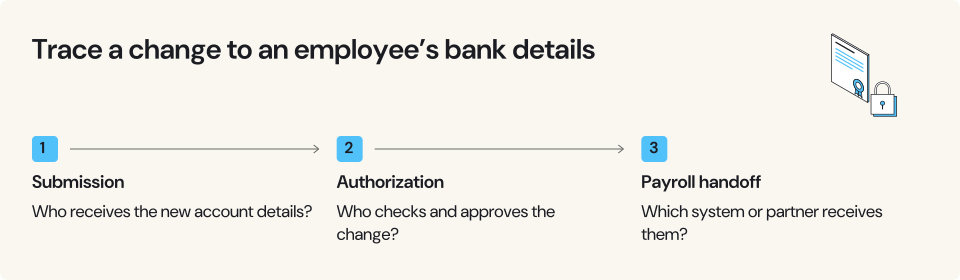
Use SOC 2 reports and ISO certificates to assess the information-security controls within their scope, and GDPR evidence to review how the provider handles personal data. Make separate checks for the EOR’s authority to employ people in each country and for the local compliance of its contracts and payroll.
2. SOC 2 Type I vs Type II: what each report covers
SOC 2 is a CPA firm’s attestation report, not a certificate, and it examines controls against the AICPA’s Trust Services Criteria. Check its scope, which may not cover every service, legal entity or security concern, and which categories it covers: security, availability, processing integrity, confidentiality and privacy.
In an EOR deal, the report type matters most:
Whether a Type I is acceptable depends on your requirements, the data involved and other assurance, not on the provider’s age alone. If your procurement policy requires a Type II, record that and ask when the provider can meet it.
Access to a restricted-use SOC 2 report may require a nondisclosure agreement or a trust-portal login. If procurement can’t inspect the report, keep the claim open and ask why access is restricted and when a reviewer can see it. Where the supplier offers a different assurance document, check what that document covers.
Inspect the scope behind a report headline
Suppose the report covers the “Core Platform” from 1 January through 31 December and excludes a local payroll partner. Find out whether that partner handles your employees’ payroll. If it does, ask for evidence covering its work and for the controls your team or another party is expected to operate alongside the provider’s.
3. How to check an ISO 27001 certificate
ISO/IEC 27001, the international standard for an information security management system (ISMS), is certifiable, unlike SOC 2. An accredited certification body (Schellman, BSI, DNV, A-LIGN and dozens of others) audits the vendor and issues a certificate valid for a 3-year cycle, with annual surveillance audits. National bodies such as ANAB (US), UKAS (UK) and DAkkS (Germany) accredit the certification bodies, and their mark should appear on the certificate.
Under the IAF accredited-certification transition, ISO 27001:2013 certificates had to expire or be withdrawn by October 31, 2025, when the International Accreditation Forum’s 3-year transition ended. Ask the certification body what evidence and assessment are required to establish a current certificate. The 2022 revision, published on October 25, 2022, restructured Annex A from 114 controls in 14 domains to 93 controls in 4 themes. It also added 11 new controls, including threat intelligence, cloud services security and data leakage prevention.
Find the scope statement on the certificate and match the named entities, systems and operations to the payroll service you’re buying. A certificate limited to corporate IT or a single office leaves the rest of that service to verify. Check the edition, validity dates and issuing body, too.
SOC 2 and ISO 27001 provide assurance in different ways. Decide whether your review needs one or both, and weigh the services covered and the evidence available over the number of badges.
4. ISO 27701: privacy management and scope
ISO/IEC 27701 covers privacy information management for personal-data controllers and processors. An EOR may be a controller for its employment obligations and a processor for other services. Base its role for each activity on what it does rather than its product label.
The 2019 edition of ISO 27701 could be held only as an add-on to an ISO 27001 certificate. ISO/IEC 27701:2025, published on October 14, 2025, is a full management system standard that can be certified on its own and adds information security controls drawn from ISO 27001. If a provider presents a 2019-edition certificate, ask its issuing body about current validity, scope and the applicable transition timetable. Do not infer validity from a trust-page badge.
As of September 2026, Papaya Global and Deel claim ISO 27701. Deel lists an ISO 27701 certificate in its trust center, though not on its main security page (checked September 2026). An ISO 27701 certificate covers privacy management within its scope; it is not a GDPR certification under Article 42. If a provider claims one, ask for the separate approved scheme and certificate.
5. GDPR certification: identify the scheme and scope
Articles 42 and 43 of the GDPR (Regulation (EU) 2016/679) set up voluntary certification for specified processing operations. Certification can support evidence of compliance but does not remove the controller’s or processor’s legal responsibilities.
Look up the scheme in the EDPB register of certification mechanisms. That tells you whether the scheme is approved. To verify the provider’s claim, you still need its certificate number, issuer, validity dates and the processing operations covered. Leave the claim marked unverified until you can check those details.
Map each party’s data-protection role, then use Article 28 terms where a provider processes data on your behalf and assess controller-to-controller or joint-controller arrangements where those roles apply. Check recipients, onward processing, transfer rules and incident contacts. A DPO or EU representative is needed only where the GDPR requires one. The data residency and SCCs guide explains the transfer questions.
Separate the two notification duties. Under Article 33, a controller must notify the competent supervisory authority without undue delay and, where feasible, within 72 hours of becoming aware, unless the breach is unlikely to risk individuals’ rights and freedoms. A processor must notify its controller without undue delay, and a contractual 72-hour allowance must not dilute that duty. Agree on prompt initial notice, follow-up information and contacts.
6. Other badges and reports: check what they cover
7. Documents to request and review
Adapt this list to your services, data and risks, and agree an evidence deadline with each vendor.
Record the outcome of each check:
- Q1. Has the evidence required by your security review been shared under agreed access terms?
- YES → Review its scope, dates and findings, then continue to Q2.
- NO → Record the claim as unverified and ask for a reason, delivery date or acceptable alternative evidence.
- Q2. If ISO 27001 is required, is the current certificate valid and does its scope cover the service?
- YES → Record the certificate details and continue to Q3.
- NO → Request current evidence and have the security reviewer assess the gap.
- Q3. Are the data recipients, their roles and the sub-processor change arrangements documented?
- YES → Continue to Q4.
- NO → Resolve the missing data flows and responsibilities before approval.
- Q4. Are data terms for each role, transfer arrangements and prompt incident-notification duties agreed?
- YES → Submit the evidence and any remaining issues for security, legal and procurement approval.
- NO → Resolve the legal and operational gaps before approval.
Cover the gap after the report period. Ask about material changes or incidents since the SOC 2 report period ended, and whether an updated report or bridge letter is available. A bridge letter is management’s statement, not a new auditor’s opinion, so agree how old a report your security review can accept. Request the documents at RFP stage. The 47-question RFP checklist includes the wider vendor questions.
Keep an assurance-review register
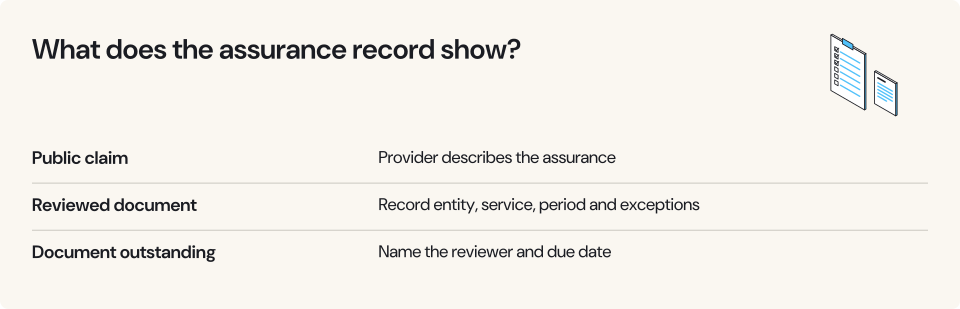
Record the entity, service, reporting period and document your team actually reviewed. Note any exceptions, controls your company must operate and parts of the proposed service outside the scope. “Requested,” “reviewed,” “expired” and “not available” belong in separate statuses so the next reviewer can see what still needs attention.
| The working record | Fields to complete |
|---|---|
The working record
Scope
|
Fields to complete
Assurance claim · Document / link · Entity and service scope
|
The working record
Evidence and follow-up
|
Fields to complete
Period / expiry · Exceptions / exclusions · Reviewer · Review outcome · Recheck date
|
8. Public assurance claims from 10 selected EOR providers
These entries record provider-published claims or dated announcements. Request the actual documents for your service.
Our provider ratings show the order in which we recommend providers overall. They are not scores for an individual fee, contract term, certification or country.
★★★★★4.7
Public SOC 2 claim
Type II
Public ISO 27001 claim
Yes
Public ISO 27701 claim
Yes (listed in its trust center, checked September 2026)
Our rating
4.7/5
Deel dashboard
Enlarge screenshot
![]()
Reviewed by Martynas Pupkevicius · Fact-checked by Michael Ennis
Opens deel.com
★★★★★4.9
Public SOC 2 claim
Type II
Public ISO 27001 claim
Yes
Public ISO 27701 claim
Not identified in the cited public material; request the document
Our rating
4.9/5
RemotePeople dashboard
Enlarge screenshot
![]()
Reviewed by Martynas Pupkevicius · Fact-checked by Michael Ennis
Opens remotepeople.com
★★★★★4.5
Public SOC 2 claim
Type II (+ SOC 1, SOC 3)
Public ISO 27001 claim
Yes
Public ISO 27701 claim
Not identified in the cited public material; request the document
Our rating
4.5/5
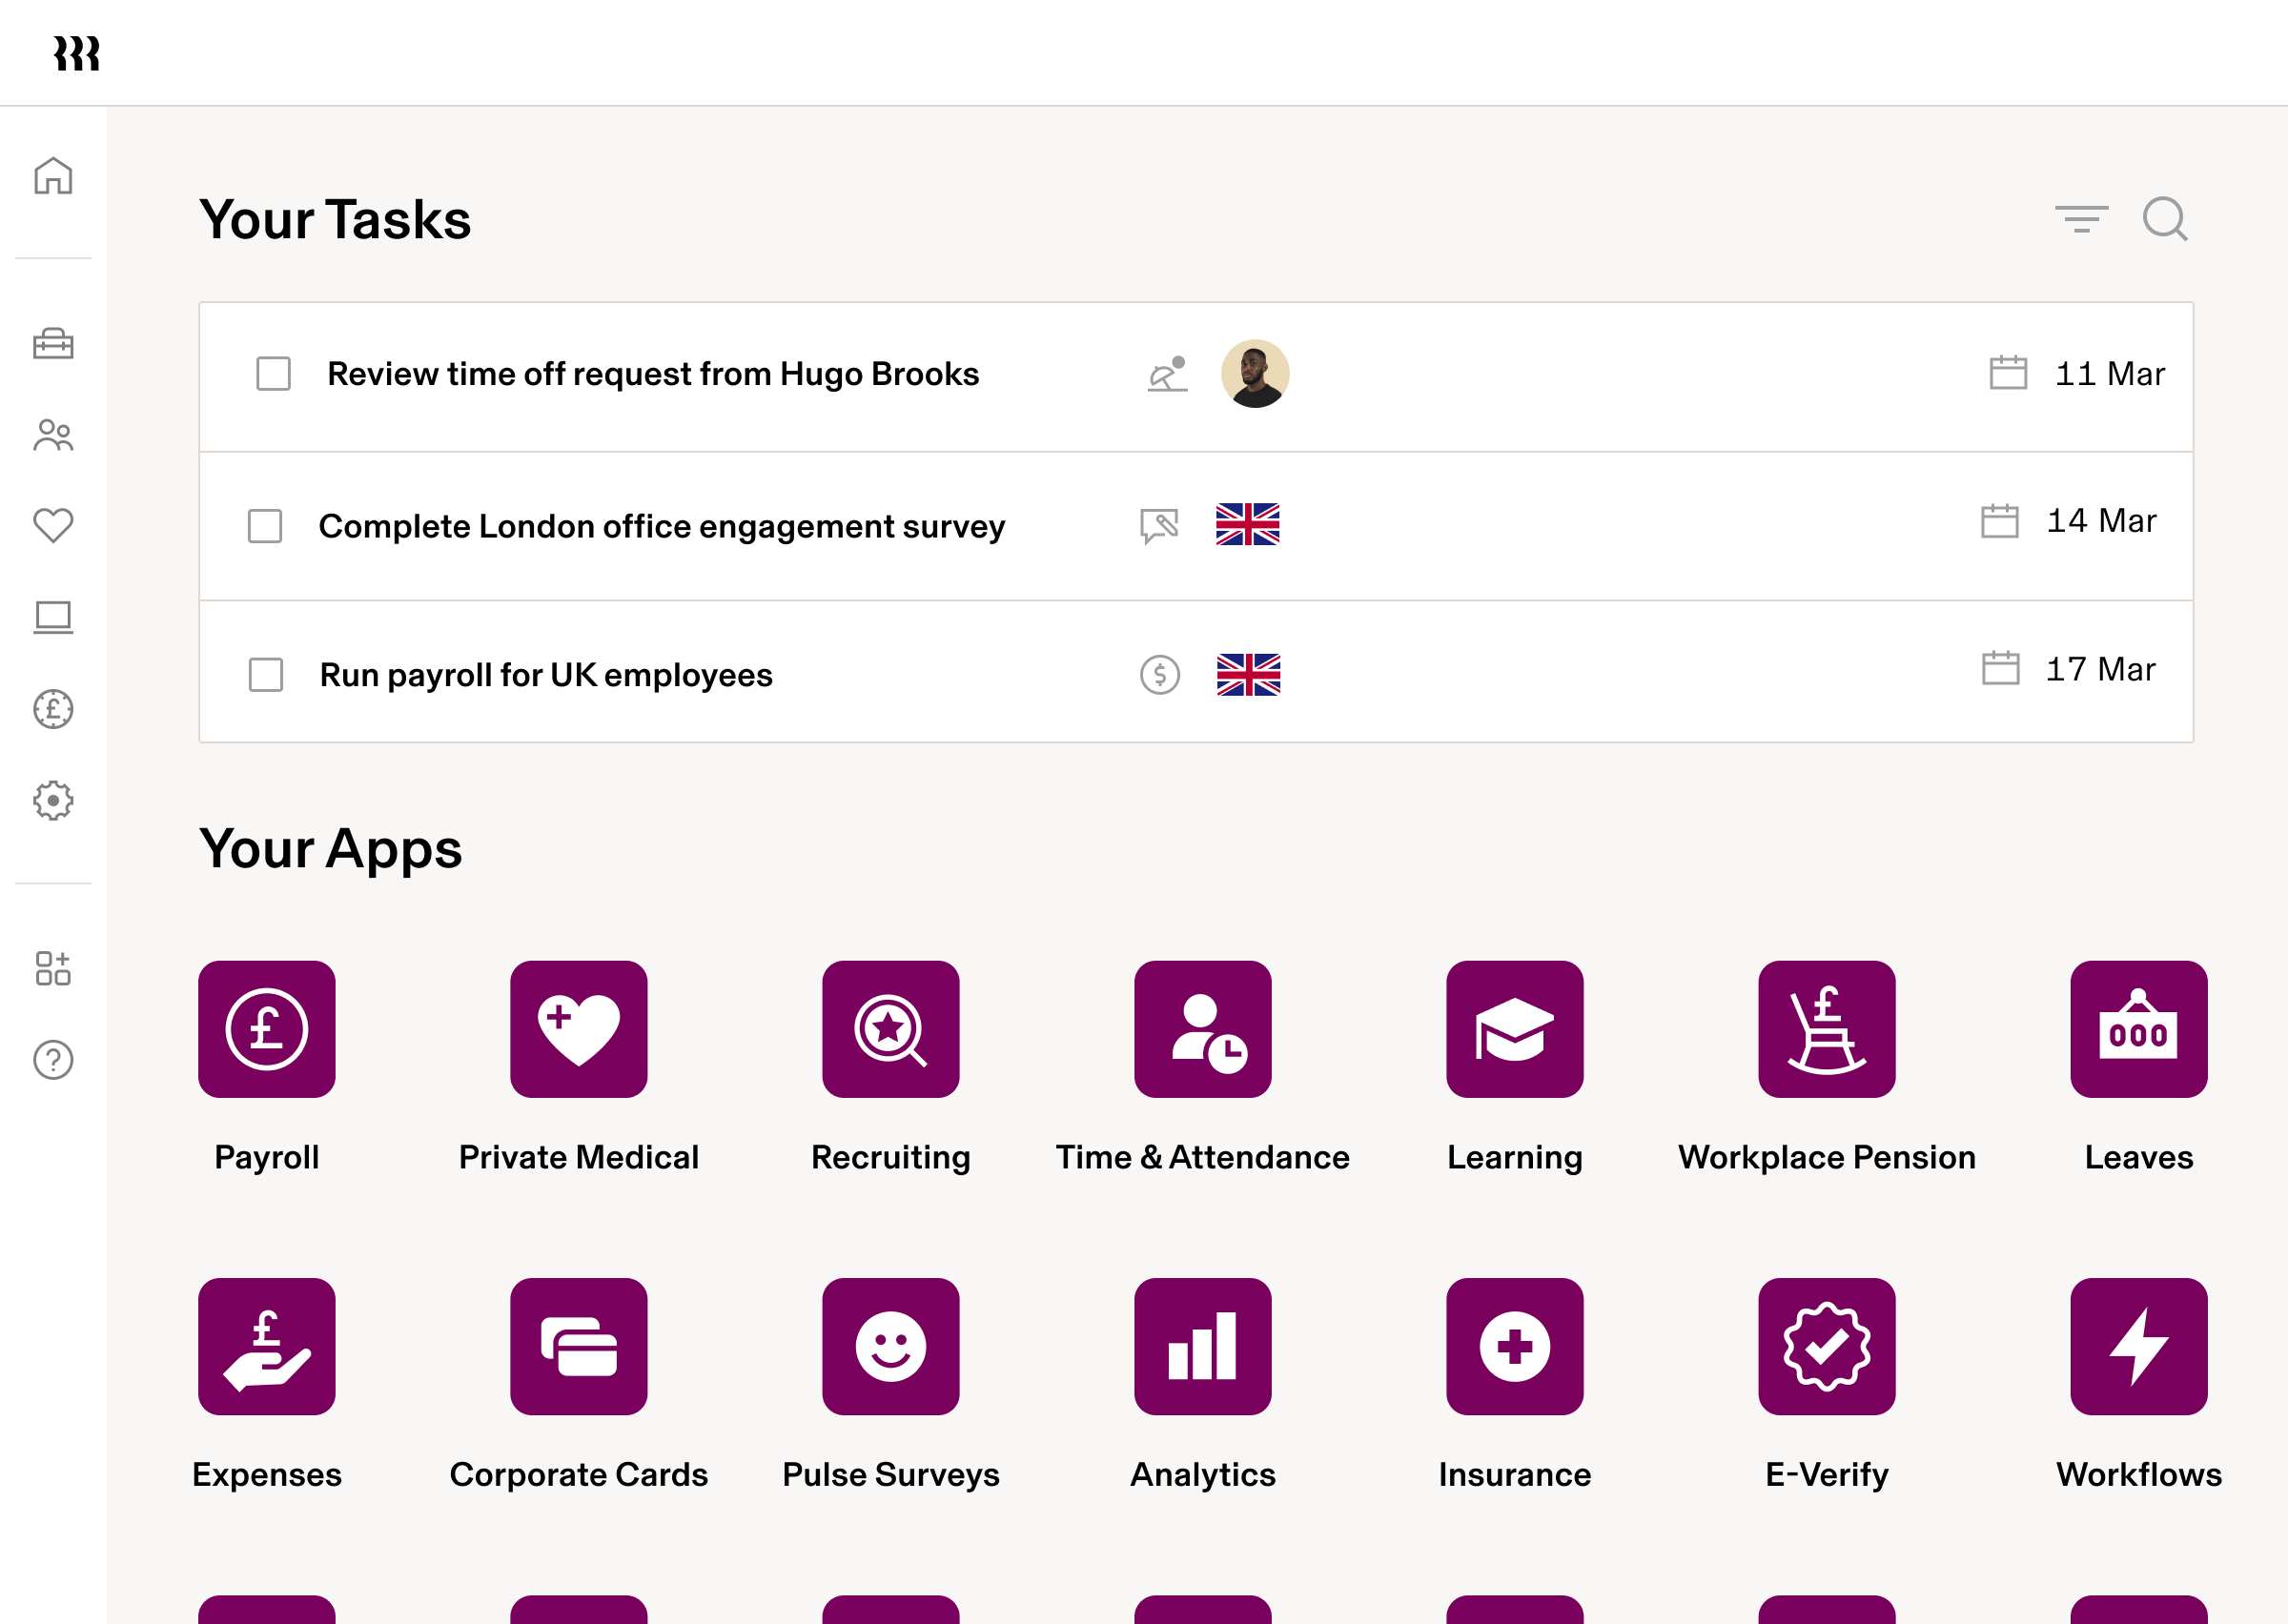
Rippling dashboard
Enlarge screenshot
![]()
Reviewed by Martynas Pupkevicius · Fact-checked by Michael Ennis
Opens rippling.com
★★★★★4.1
Public SOC 2 claim
Type II
Public ISO 27001 claim
Yes
Public ISO 27701 claim
Not identified in the cited public material; request the document
Our rating
4.1/5
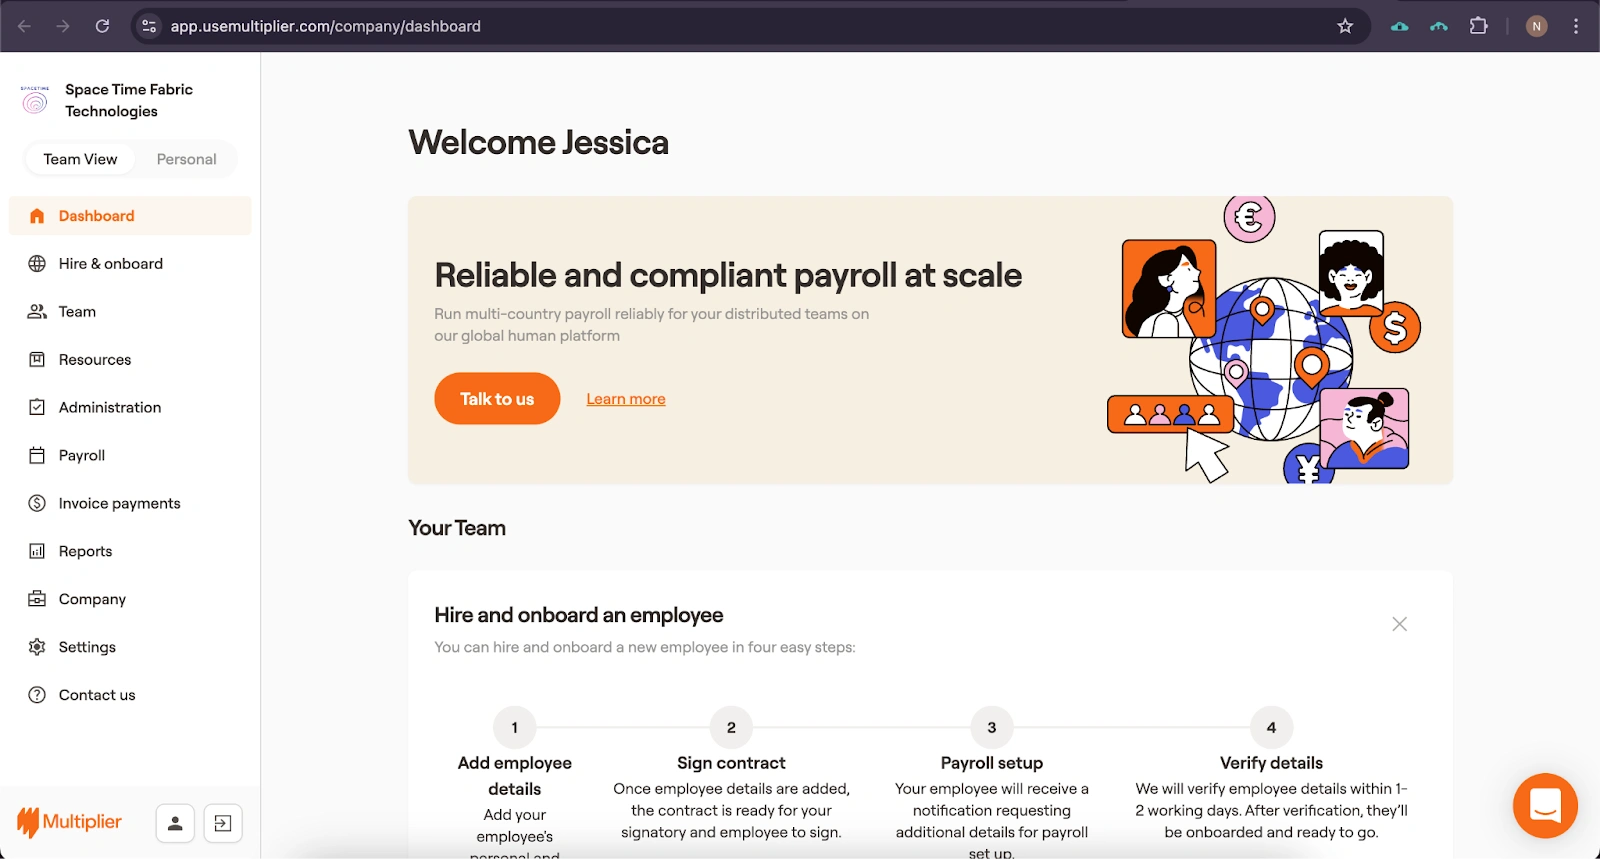
Multiplier dashboard
Enlarge screenshot
![]()
Reviewed by Martynas Pupkevicius · Fact-checked by Michael Ennis
Opens usemultiplier.com
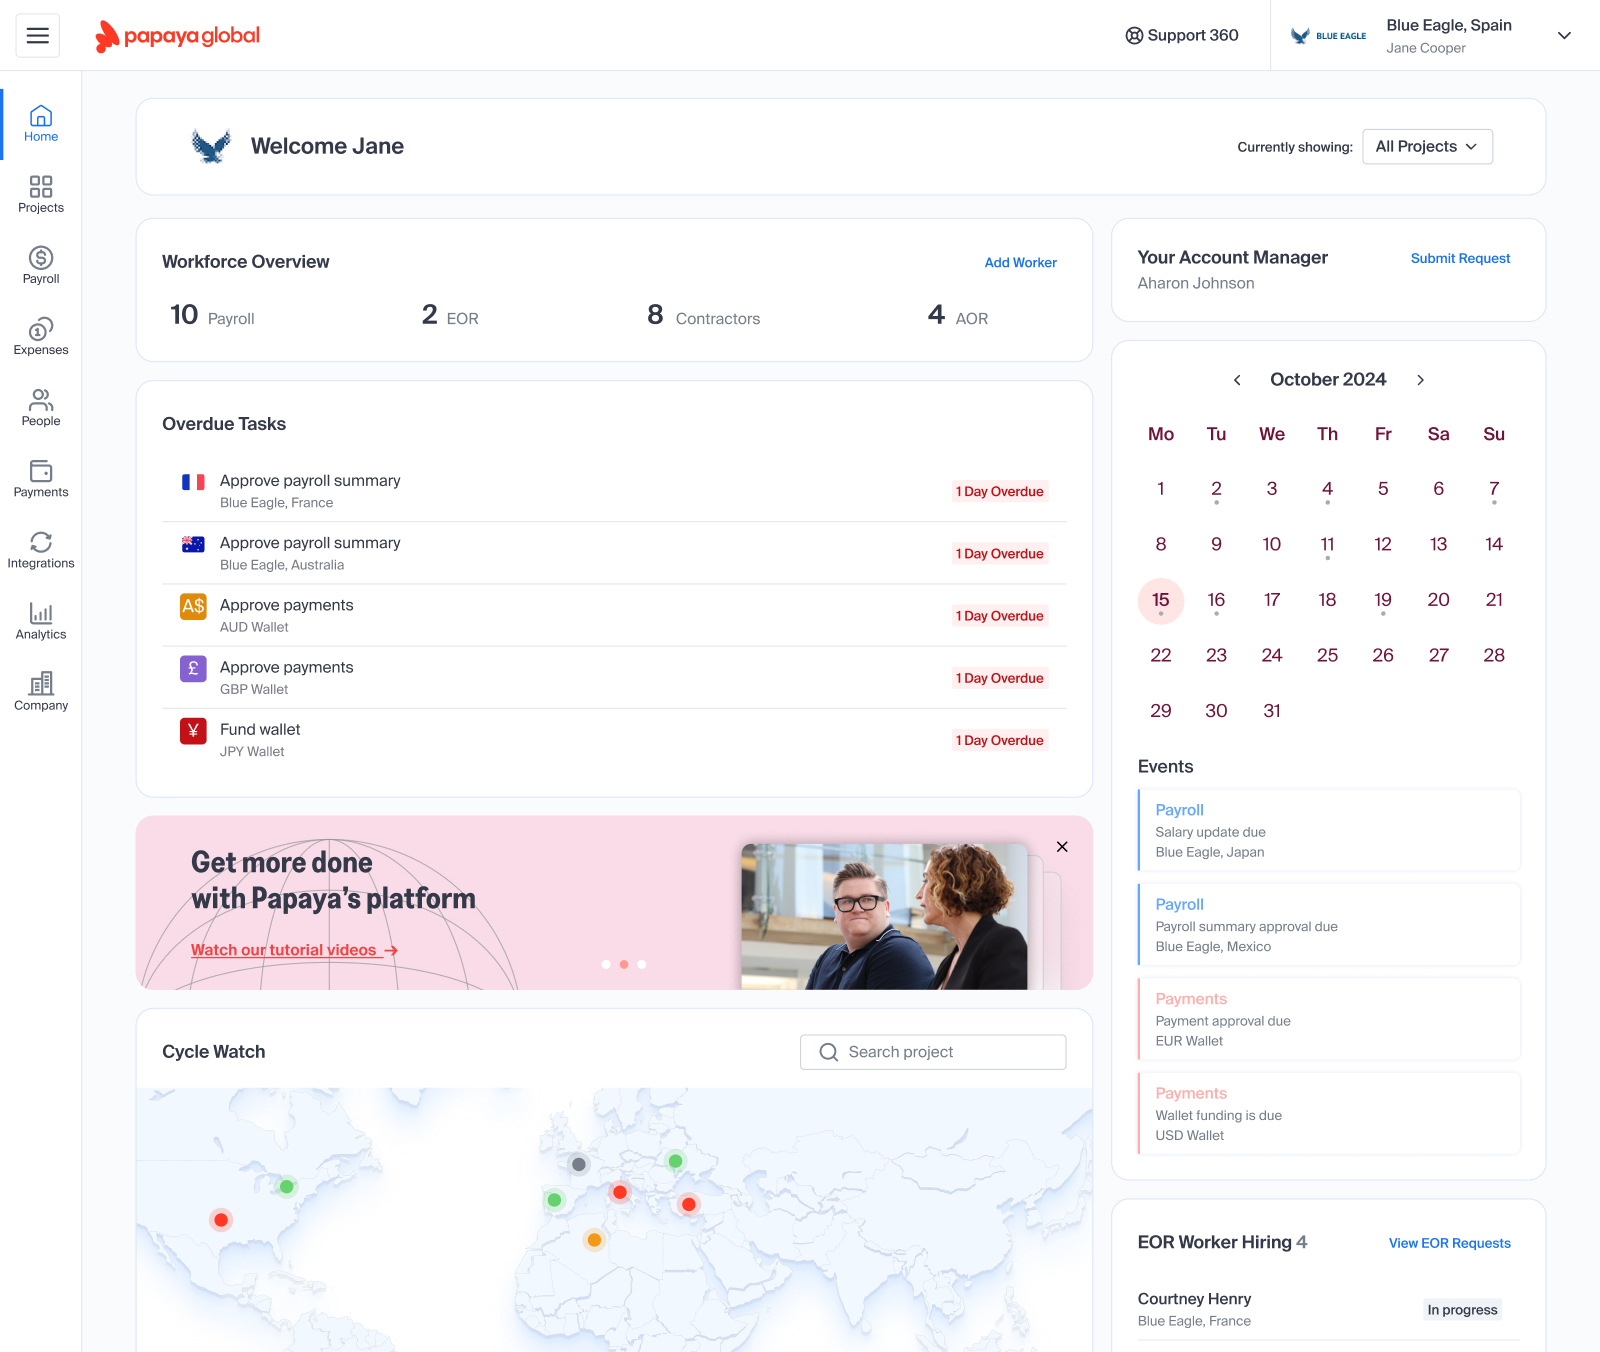
★★★★★4.1
Public SOC 2 claim
Type II (+ SOC 1 Type II)
Public ISO 27001 claim
Yes (held since 2018)
Public ISO 27701 claim
Yes
Our rating
4.1/5
Papaya Global dashboard
Enlarge screenshot
![]()
Reviewed by Martynas Pupkevicius · Fact-checked by Michael Ennis
Opens papayaglobal.com
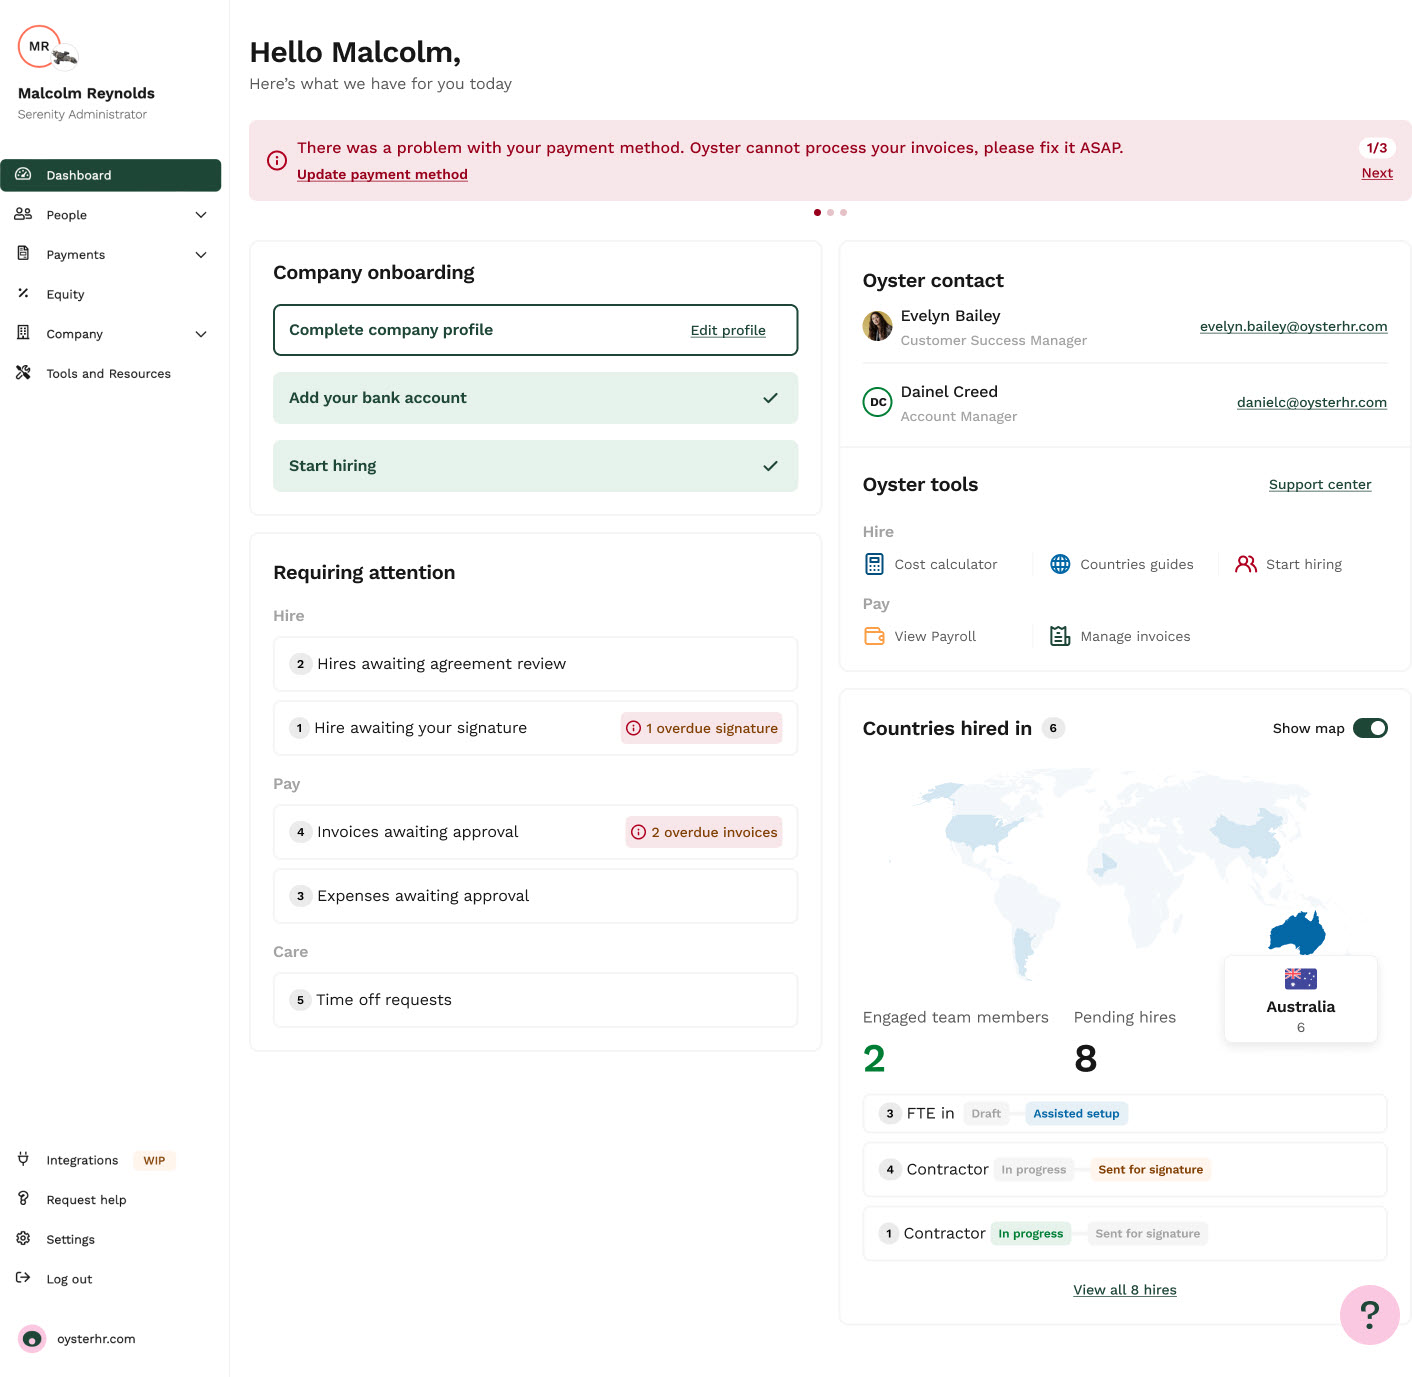
★★★★★4.5
Public SOC 2 claim
Type II
Public ISO 27001 claim
Not identified in the cited public material; request the document
Public ISO 27701 claim
Not identified in the cited public material; request the document
Our rating
4.5/5
Oyster dashboard
Enlarge screenshot
![]()
Reviewed by Martynas Pupkevicius · Fact-checked by Michael Ennis
Opens oysterhr.com
★★★★★4.2
Public SOC 2 claim
Reports maintained
Public ISO 27001 claim
Yes
Public ISO 27701 claim
Not identified in the cited public material; request the document
Our rating
4.2/5
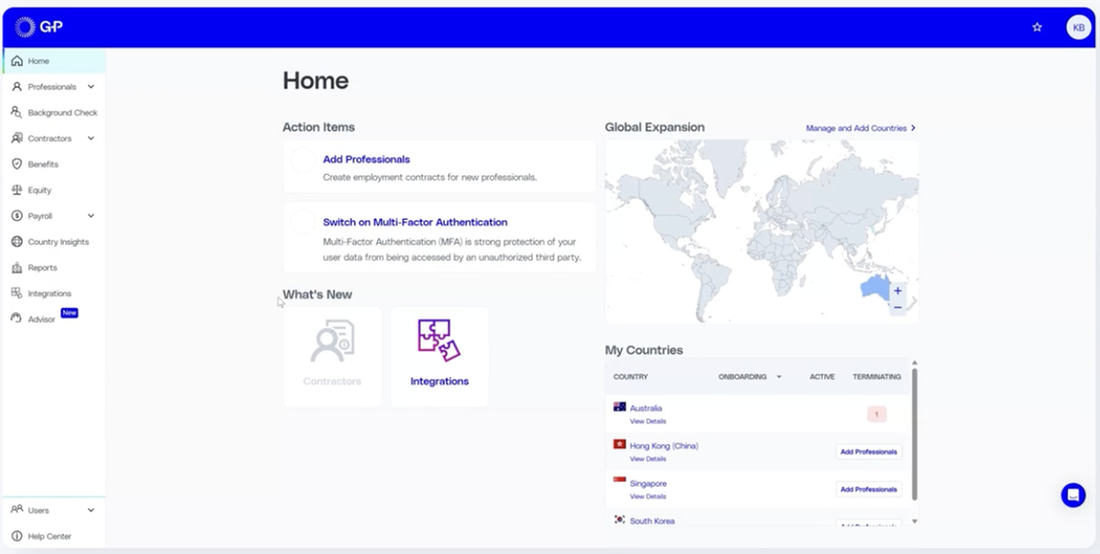
G-P dashboard
Enlarge screenshot
![]()
Reviewed by Martynas Pupkevicius · Fact-checked by Michael Ennis
Opens globalization-partners.com
★★★★★4.2
Public SOC 2 claim
Type II
Public ISO 27001 claim
Yes
Public ISO 27701 claim
Not identified in the cited public material; request the document
Our rating
4.2/5
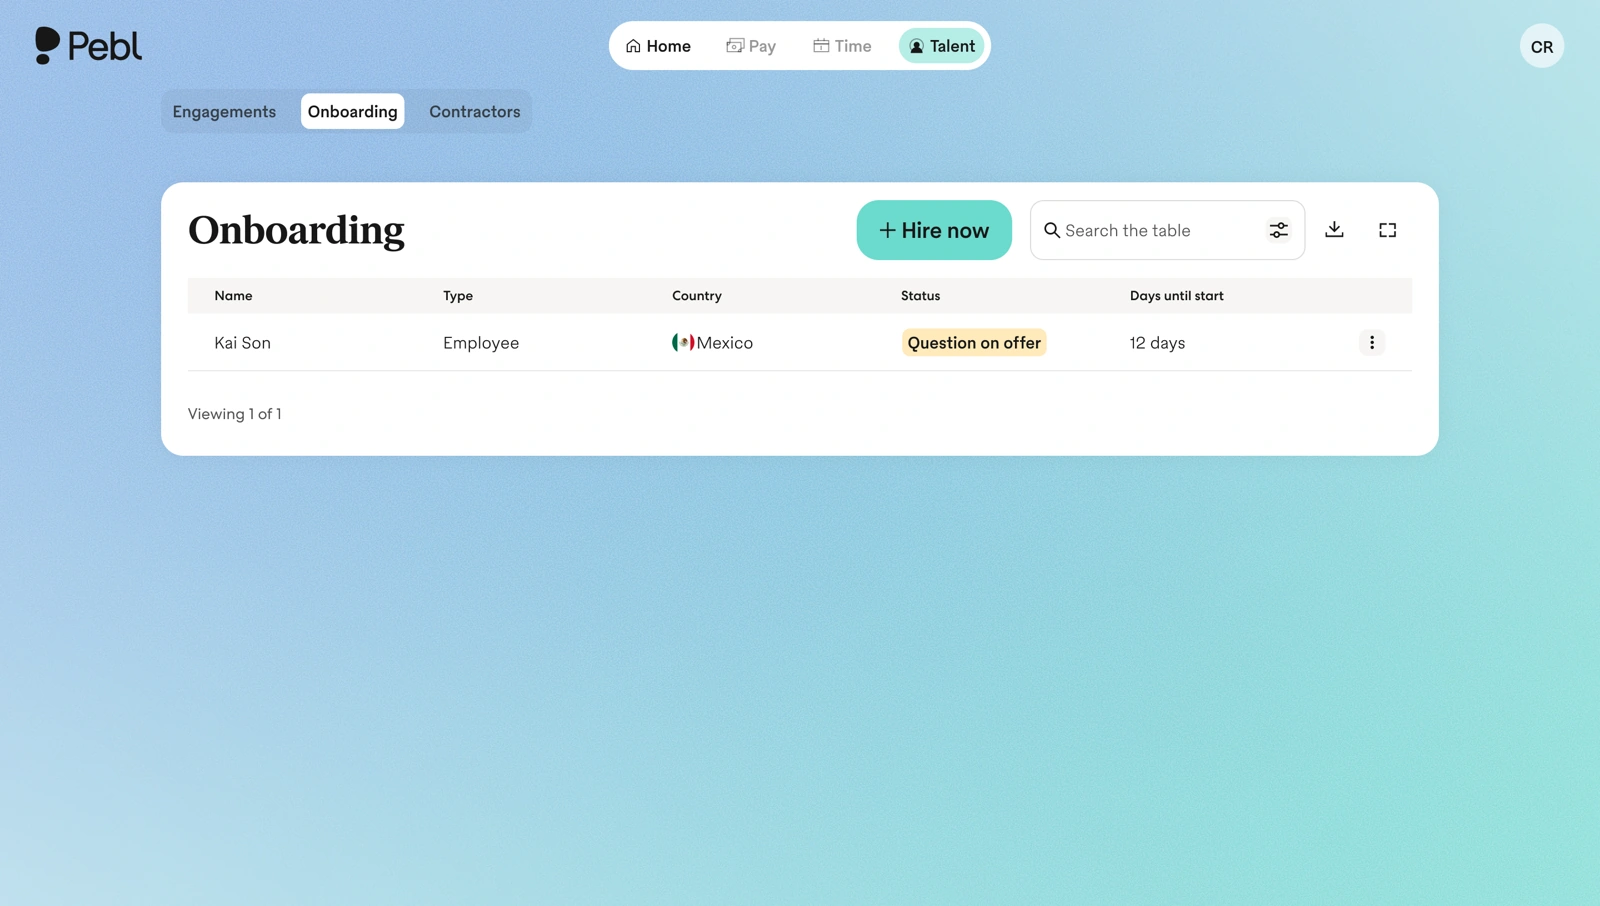
Pebl onboarding
Enlarge screenshot
![]()
Reviewed by Martynas Pupkevicius · Fact-checked by Michael Ennis
Opens hellopebl.com
★★★★★0.5
Our rating
⚠ Trustpilot warning: rating suspended for a breach of its guidelines; fake reviews removed (8 Nov 2026)
Public SOC 2 claim
Type II
Public ISO 27001 claim
Yes
Public ISO 27701 claim
Not identified in the cited public material; request the document
Our rating
0.5/5
RemoFirst dashboard
Enlarge screenshot
![]()
Reviewed by Martynas Pupkevicius · Fact-checked by Michael Ennis
Opens remofirst.com
★★★★★4.0
Public SOC 2 claim
Type II
Public ISO 27001 claim
The July 2025 announcement described certification as in progress.
Public ISO 27701 claim
Not identified in the cited public material; request the document
Our rating
4.0/5
Borderless AI dashboard
Enlarge screenshot
![]()
Reviewed by Martynas Pupkevicius · Fact-checked by Michael Ennis
Opens hireborderless.com
Fig. 1 · Public assurance claims from 10 selected providers. Historical source periods and selected 15 October 2026 webpage checks are dated by provider in the Sources section.
The labels summarize cited public statements. The actual document’s entity and service scope, reporting period or expiry, exceptions and findings determine its usefulness for your review.
Read comparison rows as evidence statuses
Use the table to decide which documents to ask for. Record the check date and distinguish a statement on a provider’s website from a current document your team has inspected. If a document hasn’t been supplied, leave the claim unverified. If a certificate has been supplied, check which processing it covers before relying on it for a GDPR review.
9. Frequently asked questions
Is SOC 2 a certification?
What is the difference between SOC 2 Type I and Type II?
A Type I covers the design of controls at a specified date, and a Type II also covers their operating effectiveness over a period. A Type I still has value, but ask which type your security policy requires, what other assurance exists and, if you need a Type II, the planned reporting period and delivery date.
Is an ISO 27001:2013 certificate still valid?
What is a SOC 2 bridge letter?
A bridge letter is management’s statement about relevant changes since the last SOC 2 reporting period ended, and it does not extend the auditor’s opinion. Ask your security reviewer whether the report’s age, the letter and other evidence are enough, or whether you need a newer report.
Can a vendor be GDPR certified?
Yes. GDPR Articles 42 and 43 provide for voluntary certification of specified processing operations, though certification does not remove the organization’s GDPR responsibilities. Check the approved scheme, issuer, certificate validity and scope. If a vendor cannot back up its claim, record it as unverified rather than assuming it is self-assessed or that no certificate exists.
10. Sources
The sources behind this guide, grouped by topic. Dates show when we last checked a page. Prices and terms change, so confirm them in your quote.
Data protection law and regulators
8 sourcesEuropean Union · EUR-Lex
GDPR Articles 28, 33, 42 and 43
Processor terms, distinct breach-notification duties and certification.
European Union · EUR-Lex
Commission Implementing Decision (EU) 2021/914
The 2021 Standard Contractual Clauses.
European Union · EDPB
Guidelines 07/2020 on controller and processor roles
The PDF is used in the certification checks, checked 3 Oct 2026.
European Union · EDPB
Guidelines 9/2022, version 2.0, on personal data breach notification
European Union · EDPB
Register of approved certification mechanisms
Tells you whether a certification scheme is approved.
European Union · EDPB
Opinions 14/2026 and 15/2026 on the Europrivacy criteria
European Data Protection Seal under Articles 42 and 46 GDPR. First approval: Opinion 28/2022.
Luxembourg · CNPD
GDPR-CARPA certification scheme
Adopted 13 May 2022.
United States · Data Privacy Framework program
Per-entity certification search
For EU-US DPF participation.
Standards and certification bodies
10 sourcesAICPA & CIMA
System and Organization Controls (SOC) suite
The Trust Services Criteria cover report scope and controls.
International · ISO
International · IAF
MD 26:2023, ISO 27001 transition requirements
Used in the certification checks. Checked 3 Oct 2026
SGS
End of the ISO/IEC 27001:2013 transition
Certification body. The transition ended on 31 October 2025 under the IAF timeline.
International · ISO
ISO/IEC 27701:2025, Privacy information management systems
Published 14 October 2025.
Schellman
Certification-body explanation; verify any applicable transition timetable with the certificate issuer.
International · ISO
ISO/IEC 27017:2026, information security controls for cloud services
International · ISO
ISO/IEC 42001, artificial intelligence management systems
Published December 2023.
Cloud Security Alliance
Level 1 is a self-assessment; Level 2 is a third-party assessment.
Europrivacy
Provider assurance claims
10 sourcesBorderless AI
The 22 July 2025 announcement states SOC 2 Type II. Request the current report and certificate evidence. Checked 15 Oct 2026
Deel
Public trust-center listing of its SOC 2 Type II report and its ISO 27001 and ISO 27701 certificates. Request the current report and certificates. Checked Sep 2026
G‑P
Historical July 2026 provider announcements. Request the current reports and certificate for the proposed service.
Multiplier
Historical July 2026 provider statements. Request current reports, certificates and entity/service scope.
Oyster
Historical July 2026 public-dashboard evidence. Verify the current report and any DPF participation for the exact entity.
Papaya Global
Historical September 2026 provider statements, including the claimed 2018 start date. Confirm the current certificate, report period and scope.
Pebl
States SOC 2 Type 2 and ISO/IEC 27001:2022. Provider claim; request the report, certificate and scope. Checked 15 Oct 2026
RemoFirst
States SOC 2 Type II and ISO 27001. Provider statement. Checked 15 Oct 2026
RemotePeople
Provider SOC 2 Type II and ISO 27001 claims. Check the actual documents and GDPR evidence for the service. Checked 15 Oct 2026
Rippling
Lists SOC reports, ISO 27001, ISO 27018, ISO 42001 and CSA STAR Level 2, which adds a third-party assessment. Request documents and scope. Checked 15 Oct 2026
Our research
2 sourcesThe Best EOR
The Best EOR
The report-type, GDPR-certification, role and notification explanations were checked on 24 Sep 2026. Provider evidence was checked in July 2026, except entries dated Sep 2026, which were checked against the providers’ own pages on 30 Sep 2026, and entries dated 15 Oct 2026, when selected public statements were refreshed.
If you spot a changed price or a conflicting source, send it through the contact page and we’ll review it.
This guide is for general information only and does not provide legal, tax, accounting, or financial advice. For advice about your business, consult a qualified professional familiar with the rules where you hire. Read our research methodology to learn how we assess sources.